Operation Endgame Seizes 235 Servers, 257 Domains; 6.4M Stolen Credentials Exposed
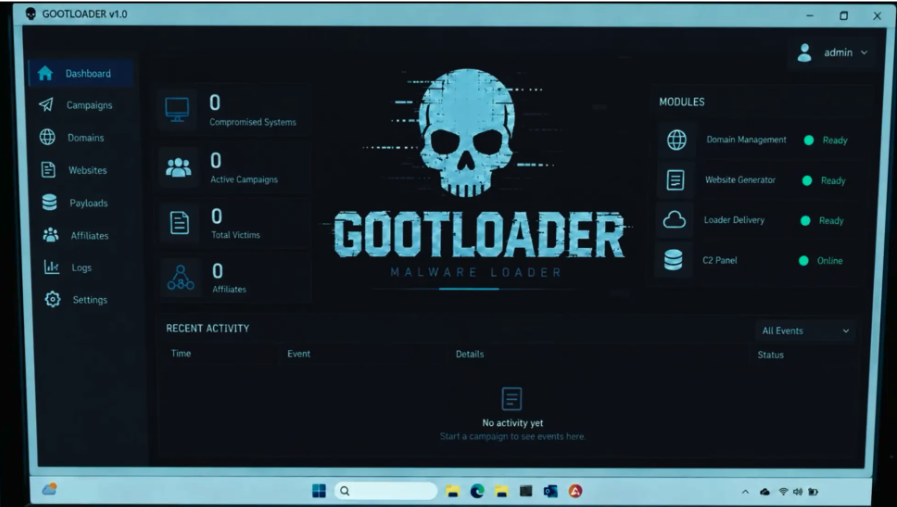
Gootloader's distribution mechanism — fake legal documents on compromised WordPress sites — means the 25,000 confirmed infections are almost certainly undercounted, since many victims would have no visibility into the initial dropper stage. If the 681 cleaned WordPress sites represent a fraction of the total seeded infrastructure, law firms and corporate legal departments remain the most exposed sector.
The DOJ's $28.8 million loss figure for Gootloader covers only confirmed US victims since 2018, so the global ransomware proceeds enabled by this access vector are substantially larger and remain unquantified.
The 6.4 million credential sets seized from StealC infrastructure represent active inventory that ransomware operators were purchasing for intrusion campaigns; removing that supply forces those operators to rebuild access pipelines from scratch.
CastleRAT's 120-server takedown is the operationally significant piece — Europol notes its anti-detection mechanisms had made it difficult to identify since 2025, meaning defenders had limited visibility into how widely it had been deployed. Victims can check exposure through HaveIBeenPwned, the Shadowserver Foundation, and the Dutch National Cyber Security Centre.
How many of the 6.4 million credential sets belonged to government or critical-infrastructure accounts versus consumer accounts — and did any of the seized StealC servers show evidence of state-linked buyers?
Fault Lines
Strategic intelligence, synthesized daily — with a public track record. Every call graded against what actually happened.