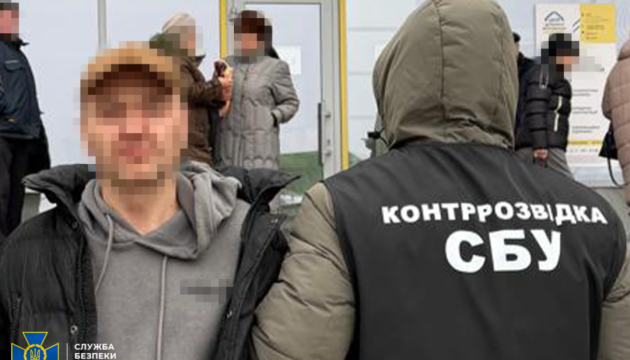
SBU Arrests Russian Agent Operating Starlink Terminal Registration Network in Ukraine
Russian efforts to penetrate Starlink's registration and control systems create a direct threat to Ukrainian military logistics and command continuity — if Moscow can register terminals under false identities, it gains legal standing to demand Starlink deactivate units during combat operations or can position terminals for capture and repurposing.
This forces SpaceX and allied governments to harden terminal authentication and registration protocols against state-level spoofing, which in turn affects how commercial satellite operators can be integrated into allied military supply chains going forward.
This incident exposes a direct Russian counterintelligence operation targeting commercial satellite infrastructure that Ukraine depends on for both civilian and military communications.
Starlink terminals have become critical for Ukrainian force coordination and resilience against Russian targeting — the FSB's effort to register units under fake identities suggests Moscow is attempting to either infiltrate the network, create legal cover for terminal seizure, or establish covert command channels.
The detention alone does not indicate how many terminals were successfully registered or whether any remain operational under Russian control; this operational gap is material to assessing the scope of the compromise.
The article does not specify: (1) how many Starlink terminals were registered under false identities before arrest; (2) whether any of these terminals are currently active or have been recovered; (3) the intended operational purpose (reconnaissance, signal intelligence, command relay, or network dis...
Fault Lines
Strategic intelligence, synthesized daily — with a public track record. Every call graded against what actually happened.